• Home
  • Insight
  • Blog
  • Business
  • Entertainment
  • Health
  • Politics
  • Shop
    • Gift Shop
    • Value Shop
    • Store
    • Bargain Shop
    • Discount
  • Sports
  • Tech
  • Travel
  • USA
  • Video
  • World
    • Asia
    • Africa
    • South America
    • North America
    • Europe
    • Oceania
Wednesday, October 7, 2026
No Result
View All Result
Subscribe Now
  • Home
  • Insight
  • Blog
  • Business
  • Entertainment
  • Health
  • Politics
  • Shop
    • Gift Shop
    • Value Shop
    • Store
    • Bargain Shop
    • Discount
  • Sports
  • Tech
  • Travel
  • USA

    Washington state man charged with helping Canadian mass shooter plan for attack

    Border Security, Public Safety, and American Sovereignty with Markwayne Mullin

    Students injured as NJ high school bleachers collapse in scary scene

    California man in incest case busted in Mexico; teen daughter rescued

    Cornell president calls gang rape allegations ‘deeply disturbing’ : NPR

    France’s violent student protests raise warning for America: ‘A cautionary tale’

    Birmingham’s WBHM Public Radio Station Forced to Use “Gulf of America”

    Eminem gets online backlash from fans over Kid Rock Christian album collab

    Trump leans into Iran war, admits it could cost Republicans the midterms

  • Video
  • World
    • Asia
    • Africa
    • South America
    • North America
    • Europe
    • Oceania
The Insight Post
  • Home
  • Insight
  • Blog
  • Business
  • Entertainment
  • Health
  • Politics
  • Shop
    • Gift Shop
    • Value Shop
    • Store
    • Bargain Shop
    • Discount
  • Sports
  • Tech
  • Travel
  • USA

    Washington state man charged with helping Canadian mass shooter plan for attack

    Border Security, Public Safety, and American Sovereignty with Markwayne Mullin

    Students injured as NJ high school bleachers collapse in scary scene

    California man in incest case busted in Mexico; teen daughter rescued

    Cornell president calls gang rape allegations ‘deeply disturbing’ : NPR

    France’s violent student protests raise warning for America: ‘A cautionary tale’

    Birmingham’s WBHM Public Radio Station Forced to Use “Gulf of America”

    Eminem gets online backlash from fans over Kid Rock Christian album collab

    Trump leans into Iran war, admits it could cost Republicans the midterms

  • Video
  • World
    • Asia
    • Africa
    • South America
    • North America
    • Europe
    • Oceania
No Result
View All Result
No Result
View All Result
Home Tech

0-days sold by Austrian firm used to hack Windows users, Microsoft says

by Theinsightpost
July 28, 2022
in Tech
0 0
0
0-days sold by Austrian firm used to hack Windows users, Microsoft says


Microsoft said on Wednesday that an Austria-based company named DSIRF used multiple Windows and Adobe Reader zero-days to hack organizations located in Europe and Central America.

Multiple news outlets have published articles like this one, which cited marketing materials and other evidence linking DSIRF to Subzero, a malicious toolset for “automated exfiltration of sensitive/private data” and “tailored access operations [including] identification, tracking and infiltration of threats.”

Members of the Microsoft Threat Intelligence Center, or MSTIC, said they have found Subzero malware infections spread through a variety of methods, including the exploitation of what at the time were Windows and Adobe Reader zero-days, meaning the attackers knew of the vulnerabilities before Microsoft and Adobe did. Targets of the attacks observed to date include law firms, banks, and strategic consultancies in countries such as Austria, the UK, and Panama, although those aren’t necessarily the countries in which the DSIRF customers who paid for the attack resided.

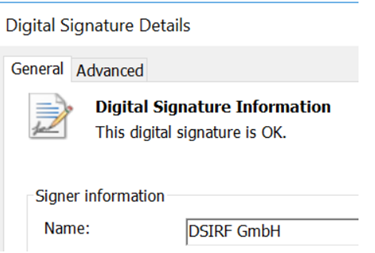
“MSTIC has found multiple links between DSIRF and the exploits and malware used in these attacks,” Microsoft researchers wrote. “These include command-and-control infrastructure used by the malware directly linking to DSIRF, a DSIRF-associated GitHub account being used in one attack, a code signing certificate issued to DSIRF being used to sign an exploit, and other open source news reports attributing Subzero to DSIRF.”
Microsoft

An email sent to DSIRF seeking comment wasn’t returned.

Advertisement

Wednesday’s post is the latest to take aim at the scourge of mercenary spyware sold by private companies. Israel-based NSO Group is the best-known example of a for-profit company selling pricey exploits that often compromise the devices belonging to journalists, attorneys, and activists. Another Israel-based mercenary named Candiru was profiled by Microsoft and University of Toronto’s Citizen Lab last year and was recently caught orchestrating phishing campaigns on behalf of customers that could bypass two-factor authentication.

Also on Wednesday, the US House of Representatives Permanent Select Committee on Intelligence held a hearing on the proliferation of foreign commercial spyware. One of the speakers was the daughter of a former hotel manager in Rwanda who was imprisoned after saving hundreds of lives and speaking out about the genocide that had taken place. She recounted the experience of having her phone hacked with NSO spyware the same day she met with the Belgian foreign affairs minister.

Referring to DSIRF using the work KNOTWEED, Microsoft researchers wrote:

In May 2022, MSTIC found an Adobe Reader remote code execution (RCE) and a 0-day Windows privilege escalation exploit chain being used in an attack that led to the deployment of Subzero. The exploits were packaged into a PDF document that was sent to the victim via email. Microsoft was not able to acquire the PDF or Adobe Reader RCE portion of the exploit chain, but the victim’s Adobe Reader version was released in January 2022, meaning that the exploit used was either a 1-day exploit developed between January and May, or a 0-day exploit. Based on KNOTWEED’s extensive use of other 0-days, we assess with medium confidence that the Adobe Reader RCE is a 0-day exploit. The Windows exploit was analyzed by MSRC, found to be a 0-day exploit, and then patched in July 2022 as CVE-2022-22047. Interestingly, there were indications in the Windows exploit code that it was also designed to be used from Chromium-based browsers, although we’ve seen no evidence of browser-based attacks.

The CVE-2022-22047 vulnerability is related to an issue with activation context caching in the Client Server Run-Time Subsystem (CSRSS) on Windows. At a high level, the vulnerability could enable an attacker to provide a crafted assembly manifest, which would create a malicious activation context in the activation context cache, for an arbitrary process. This cached context is used the next time the process spawned.

CVE-2022-22047 was used in KNOTWEED related attacks for privilege escalation. The vulnerability also provided the ability to escape sandboxes (with some caveats, as discussed below) and achieve system-level code execution. The exploit chain starts with writing a malicious DLL to disk from the sandboxed Adobe Reader renderer process. The CVE-2022-22047 exploit was then used to target a system process by providing an application manifest with an undocumented attribute that specified the path of the malicious DLL. Then, when the system process next spawned, the attribute in the malicious activation context was used, the malicious DLL was loaded from the given path, and system-level code execution was achieved.

Wednesday’s post also provides detailed indicators of compromise that readers can use to determine if they have been targeted by DSIRF.

Advertisement

Microsoft used the term PSOA—short for private-sector offensive actor—to describe cyber mercenaries like DSIRF. The company said most PSOAs operate under one or both of two models. The first, access-as-a-service, sells full end-to-end hacking tools to customers for use in their own operations. In the other model, hack-for-hire, the PSOA carries out the targeted operations itself.

“Based on observed attacks and news reports, MSTIC believes that KNOTWEED may blend these models: they sell the Subzero malware to third parties but have also been observed using KNOTWEED-associated infrastructure in some attacks, suggesting more direct involvement,” Microsoft researchers wrote.


Source link

ShareTweetSend
Previous Post

Poll: High gas prices hit Black, Latino Californians hardest

Next Post

Sam Burgess rejects Dolphins to return to South Sydney Rabbitohs

Related News

Tech

Spotify expands audiobooks to over 180 markets

October 7, 2026
Tech

You Probably Aren’t Going to Get the Plague

October 6, 2026
Tech

Sources: the FBI removes an Accenture contractor over a breach exposing thousands of employees’ data; the FBI says a contractor failed to apply a security patch (Reuters)

October 6, 2026
Tech

Amazon hires a veteran Microsoft AI leader to help build its tools for coding and work

October 5, 2026
Next Post
Sam Burgess rejects Dolphins to return to South Sydney Rabbitohs

Sam Burgess rejects Dolphins to return to South Sydney Rabbitohs

Discussion about this post

Subscribe To Our Newsletters

    Customer Support


    1251 Wilcrest Drive
    Houston, Texas
    77042 USA
    Call-832.795.1420
    e-mail – news@theinsightpost.com

    Subscribe To Our Newsletters

      Categories

      • Africa
      • Africa-East
      • African Sports
      • American Sports
      • Arts
      • Asia
      • Australia
      • Business
      • Business Asia
      • Business- Africa
      • Canada
      • Defense
      • Education
      • Egypt
      • Energy
      • Entertainment
      • Europe
      • European Soccer
      • Finance
      • Germany
      • Ghana
      • Health
      • Insight
      • International
      • Investing
      • Japan
      • Latest Headlines
      • Life & Living
      • Markets
      • Mobile
      • Movies
      • New Zealand
      • Nigeria
      • Politics
      • Scholarships
      • Science
      • South Africa
      • South America
      • Sports
      • Tech
      • Travel
      • UK
      • USA
      • Weather
      • World
      No Result
      View All Result

      Recent News

      Boxing legend Mike Tyson talks going to juvie and trading cigarettes for cookies as a young boy

      October 7, 2026

      Hogbetsotso 2026 to promote tourism, local businesses

      October 7, 2026

      Mikel Arteta’s new contract: The challenges facing Arsenal boss as he enters ‘step five’ of his project | Football News

      October 7, 2026

      Spotify expands audiobooks to over 180 markets

      October 7, 2026
      • Home
      • Advertise With Us
      • About Us
      • Corporate
      • Consumer Rewards
      • Forum
      • Privacy Policy
      • Social Trends

      Theinsightpost ©2026 | All Rights Reserved. Theinsightpost is an Elnegy LLC company, registered in Texas, USA

      Welcome Back!

      Login to your account below

      Forgotten Password?

      Retrieve your password

      Please enter your username or email address to reset your password.

      Log In

      Add New Playlist

      We are using cookies to give you the best experience on our website.

      You can find out more about which cookies we are using or switch them off in .

      No Result
      View All Result
      • Home
      • Insight
      • Blog
      • Business
      • Entertainment
      • Health
      • Politics
      • Shop
        • Gift Shop
        • Value Shop
        • Store
        • Bargain Shop
        • Discount
      • Sports
      • Tech
      • Travel
      • USA
      • Video
      • World
        • Asia
        • Africa
        • South America
        • North America
        • Europe
        • Oceania

      Theinsightpost ©2026 | All Rights Reserved. Theinsightpost is an Elnegy LLC company, registered in Texas, USA

      The Insight Post
      Powered by  GDPR Cookie Compliance
      Privacy Overview

      This website uses cookies so that we can provide you with the best user experience possible. Cookie information is stored in your browser and performs functions such as recognising you when you return to our website and helping our team to understand which sections of the website you find most interesting and useful.

      Strictly Necessary Cookies

      Strictly Necessary Cookie should be enabled at all times so that we can save your preferences for cookie settings.

      Cookie Policy

      More information about our Cookie Policy

      Clear examples do more than decorate an explanation: they show how an idea behaves under recognizable conditions. In education and software documentation alike, strong illustrations begin with a defined goal, then reveal the steps, assumptions, and result without unnecessary detail. A practical test example should state the input, expected output, and boundary condition, because these elements show whether a rule works beyond the simplest case. Including a contrasting case also helps readers distinguish a valid application from a tempting but incorrect one, while concise notes explain why the outcomes differ. When examples are updated with current data and checked against the underlying rule, they remain useful across classrooms, product guides, and professional training.