• Home
  • Insight
  • Blog
  • Business
  • Entertainment
  • Health
  • Politics
  • Shop
    • Gift Shop
    • Value Shop
    • Store
    • Bargain Shop
    • Discount
  • Sports
  • Tech
  • Travel
  • USA
  • Video
  • World
    • Asia
    • Africa
    • South America
    • North America
    • Europe
    • Oceania
Wednesday, November 18, 2026
No Result
View All Result
Subscribe Now
  • Home
  • Insight
  • Blog
  • Business
  • Entertainment
  • Health
  • Politics
  • Shop
    • Gift Shop
    • Value Shop
    • Store
    • Bargain Shop
    • Discount
  • Sports
  • Tech
  • Travel
  • USA
    Mary Peltola Emerges Victorious in Alaska Senate Race, Making History for Democrats

    Mary Peltola Emerges Victorious in Alaska Senate Race, Making History for Democrats

    Stranded in Conflict: Palestinians Navigate the Tenuous Balance of War and Peace Amid Ceasefire Efforts

    Stranded in Conflict: Palestinians Navigate the Tenuous Balance of War and Peace Amid Ceasefire Efforts

    Trump Administration Revokes Pay Increase for Head Start Educators

    Trump Administration Revokes Pay Increase for Head Start Educators

    Unexpected Triumph: Gay Candidates Achieve Unforeseen Victories in Challenging Races

    Unexpected Triumph: Gay Candidates Achieve Unforeseen Victories in Challenging Races

    Microsoft Outlook Experiences Prolonged Outage Affecting Users Nationwide

    Microsoft Outlook Experiences Prolonged Outage Affecting Users Nationwide

    Gunfire Erupts in D.C.: Authorities Search for Suspect Amid Rising Concerns Over Public Safety

    Gunfire Erupts in D.C.: Authorities Search for Suspect Amid Rising Concerns Over Public Safety

    LAUSD Takes Strong Action Against Hate Speech Following Racial Slur Incidents

    LAUSD Takes Strong Action Against Hate Speech Following Racial Slur Incidents

    Beloved Former Los Angeles Times Columnist Steve Harvey Passes Away at 80

    Beloved Former Los Angeles Times Columnist Steve Harvey Passes Away at 80

    Exploring Diversity: ‘Ten Lives’ Showcases the Varied Economic Journeys of Americans

    Exploring Diversity: ‘Ten Lives’ Showcases the Varied Economic Journeys of Americans

  • Video
  • World
    • Asia
    • Africa
    • South America
    • North America
    • Europe
    • Oceania
The Insight Post
  • Home
  • Insight
  • Blog
  • Business
  • Entertainment
  • Health
  • Politics
  • Shop
    • Gift Shop
    • Value Shop
    • Store
    • Bargain Shop
    • Discount
  • Sports
  • Tech
  • Travel
  • USA
    Mary Peltola Emerges Victorious in Alaska Senate Race, Making History for Democrats

    Mary Peltola Emerges Victorious in Alaska Senate Race, Making History for Democrats

    Stranded in Conflict: Palestinians Navigate the Tenuous Balance of War and Peace Amid Ceasefire Efforts

    Stranded in Conflict: Palestinians Navigate the Tenuous Balance of War and Peace Amid Ceasefire Efforts

    Trump Administration Revokes Pay Increase for Head Start Educators

    Trump Administration Revokes Pay Increase for Head Start Educators

    Unexpected Triumph: Gay Candidates Achieve Unforeseen Victories in Challenging Races

    Unexpected Triumph: Gay Candidates Achieve Unforeseen Victories in Challenging Races

    Microsoft Outlook Experiences Prolonged Outage Affecting Users Nationwide

    Microsoft Outlook Experiences Prolonged Outage Affecting Users Nationwide

    Gunfire Erupts in D.C.: Authorities Search for Suspect Amid Rising Concerns Over Public Safety

    Gunfire Erupts in D.C.: Authorities Search for Suspect Amid Rising Concerns Over Public Safety

    LAUSD Takes Strong Action Against Hate Speech Following Racial Slur Incidents

    LAUSD Takes Strong Action Against Hate Speech Following Racial Slur Incidents

    Beloved Former Los Angeles Times Columnist Steve Harvey Passes Away at 80

    Beloved Former Los Angeles Times Columnist Steve Harvey Passes Away at 80

    Exploring Diversity: ‘Ten Lives’ Showcases the Varied Economic Journeys of Americans

    Exploring Diversity: ‘Ten Lives’ Showcases the Varied Economic Journeys of Americans

  • Video
  • World
    • Asia
    • Africa
    • South America
    • North America
    • Europe
    • Oceania
No Result
View All Result
No Result
View All Result
Home Tech

Software developers have a supply chain security problem

by Theinsightpost
July 13, 2022
in Tech
0 0
0
Software developers have a supply chain security problem


Log4j was the bucket of cold water that woke up most developers to their software supply chain security problem. 

We’ve spent decades in software building things and obsessing over our production environment. But we’re building on unpatched Jenkins boxes sitting under someone’s desk. We spend all this time protecting our runtimes, then deploy to them using amateur tooling. 

Our build environments aren’t nearly as secure as our production environments.

That’s what led to a whole lot of high-profile attacks in the last 12 months, from SolarWinds, to the Codecov attack, to the Travis CI secrets leak. We’ve gotten so good at protecting our infrastructure that attackers looked for an easier way in, and found it in the doorways we’ve left open in the supply chain.

Can’t get in through the perimeter security? Just find an open source dependency, or a library, and get in that way. Then pivot to all of the customers. This is the modern software supply chain hack.

We need roots of trust for software

We have roots of trust for people today. We have two-factor authentication, we have identification systems. These are things to vouch for a person’s identity. And hardware has the same thing. We have encryption keys. We have hardware we can trust hasn’t been tampered with when it boots up.

Even as internet users we have roots of trust. We have URIs, URNs, and URLs—effectively the namespaces on the internet that connect the identities, names, and locations of sites we are browsing. SSL certificates tell our browsers that sites are secure. DNS firewalls sit between the user’s recursive resolvers to make sure our cache isn’t being loaded with bad requests. All of this is happening behind the scenes, and has been incredibly effective in supporting billions of internet users for decades.

But we don’t have this for software artifacts today. 

Developers trust too much implicitly

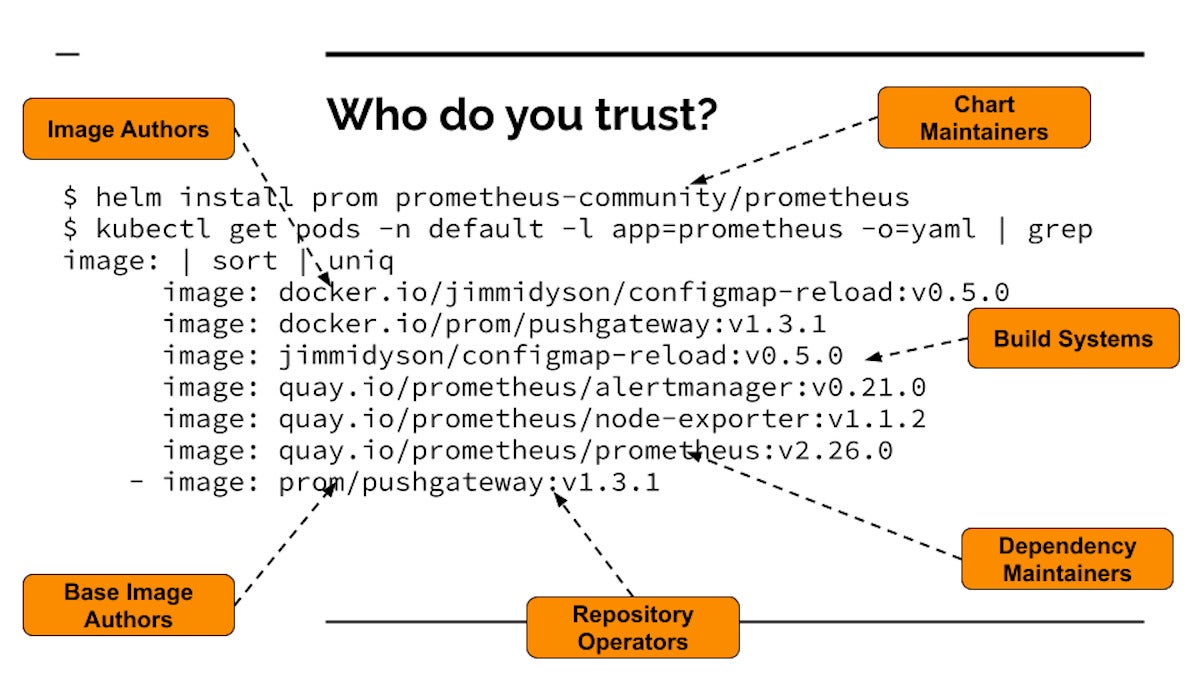
Take an event as commonplace as installing Prometheus (a popular open source observability project) from the Cloud Native Computing Foundation (CNCF) artifact hub. If you do your Helm install and then look at all the images that get pulled and start running your cluster, you see many container images that end up running from a simple installation. Developers are entrusting a whole bunch of things to a whole bunch of different people and systems. Every single one of these could be tampered with or attacked, or could be malicious.
zero trust supply chain security Dan Lorenc

This is the opposite of Zero Trust—we’re trusting dozens of systems that we don’t know anything about. We don’t know the authors, we don’t know if the code is malicious, and because each image has its own artifacts, the whole supply chain is recursive. So we’re not only trusting the artifacts, but also the people who trusted the dependencies of these artifacts.

We’re also trusting the people who operate the repositories. So if the repository operators get compromised, now the compromisers are part of your trust circle. Anybody controlling one of these repositories could change something and attack you. 

Then there’s the build systems. Build systems can get attacked and insert malicious code. That’s exactly what happened with SolarWinds. Even if you know and trust the operators of the images, and the people operating the systems that host the images, if these are built insecurely, then some malware can get inserted. And again it’s recursive all the way down. The dependency maintainers, the build systems they use, the artifact managers that they are hosted on—they’re all undermined.

So when developers install software packages, there are a lot of things they are trusting implicitly, whether they mean to trust them or not.

Software supply chain security gotchas

The worst strategy you can have in software supply chain security is to do nothing, which is what a lot of developers are doing today. They are allowing anything to run on production environments. If you have no security around what artifacts can run, then you have no idea where they came from. This is the worst of the worst. This is not paying attention at all.

Allow-listing specific tags is the next level up. If you go through some of the tutorials around best practices with Kubernetes, this is pretty easy to set up. If you push all your images to a single location, you can at least restrict things to that location. That’s way better than doing nothing, but it’s still not great, because then anything that gets pushed there is now inside your trust circle, inside that barbed wire fence, and that’s not really Zero Trust. Allow-listing specific repositories has all the same limitations of allow-listing specific tags.

Even the signing schemas in supply chain security are papering over the same problem. Anything that gets signed now gets to run, regardless of where it came from, which leads to tons of attacks tied to tricking someone to sign the wrong thing, or being unable to revoke a certificate.

Time to start asking the right questions

Let’s say you’re walking down the sidewalk outside of your office, and you find a USB thumb drive sitting on the ground. I hope everyone knows that you should absolutely not take that drive inside your office and plug it into your workstation. Everyone in software should (rightly) be screaming, “No!” Real attacks have happened this way, and security orgs across the world hammer this warning into all employees as part of training.

But for some reason, we don’t even pause to think twice before running docker pull or npm install, even though these are arguably worse than plugging in a random USB stick. Both situations involve taking code from someone you do not trust and running it, but the Docker container or NPM package will eventually make it all the way into your production environment!

The essence of this supply chain security evolution is that as an industry we’re moving away from trusting where the software artifacts come from, and spending much more time figuring out roots of trust for what the artifact is.

Who published this binary? How was it built? What version of the tool was used? What source was it built from? Who signed off on this code? Was anything tampered with? These are the right questions to be asking.

Next week, we’ll look at the fast-evolving open source landscape that is forming a new security stack for supply chain security, and unpack essential concepts developers need to understand—from roots of trust, to provenance, to TPM (Trusted Platform Module) attestation.

Dan Lorenc is CEO and co-founder of Chainguard. Previously he was staff software engineer and lead for Google’s Open Source Security Team (GOSST). He has founded projects like Minikube, Skaffold, TektonCD, and Sigstore.

—

New Tech Forum provides a venue to explore and discuss emerging enterprise technology in unprecedented depth and breadth. The selection is subjective, based on our pick of the technologies we believe to be important and of greatest interest to InfoWorld readers. InfoWorld does not accept marketing collateral for publication and reserves the right to edit all contributed content. Send all inquiries to newtechforum@infoworld.com.

Copyright © 2022 IDG Communications, Inc.



Source link

ShareTweetSend
Previous Post

Senate Democrats unveil abortion access bill ‘Freedom to Travel For Health Act of 2022′

Next Post

Byju’s Pondicherry T10 Tournament 2022 Points Table and Team Standings

Related News

Transform Your Laptop Setup with These 5 Affordable Accessories
Tech

Transform Your Laptop Setup with These 5 Affordable Accessories

November 15, 2026
Microsoft 365 Services Gradually Restore Functionality Following Global Outage
Tech

Microsoft 365 Services Gradually Restore Functionality Following Global Outage

November 14, 2026
Epic Seeks Accountability for Apple’s Alleged Disregard of Court Ruling Intent
Tech

Epic Seeks Accountability for Apple’s Alleged Disregard of Court Ruling Intent

November 13, 2026
European Cybersecurity Firms Make Strides Against U.S. Competitors, Yet American Companies Still Command 62% of the Market
Tech

European Cybersecurity Firms Make Strides Against U.S. Competitors, Yet American Companies Still Command 62% of the Market

November 13, 2026
Next Post
Byju’s Pondicherry T10 Tournament 2022 Points Table and Team Standings

Byju’s Pondicherry T10 Tournament 2022 Points Table and Team Standings

Discussion about this post

Subscribe To Our Newsletters

    Customer Support


    1251 Wilcrest Drive
    Houston, Texas
    77042 USA
    Call-832.795.1420
    e-mail – news@theinsightpost.com

    Subscribe To Our Newsletters

      Categories

      • Africa
      • Africa-East
      • African Sports
      • American Sports
      • Arts
      • Asia
      • Australia
      • Business
      • Business Asia
      • Business- Africa
      • Canada
      • Defense
      • Education
      • Egypt
      • Energy
      • Entertainment
      • Europe
      • European Soccer
      • Finance
      • Germany
      • Ghana
      • Health
      • Insight
      • International
      • Investing
      • Japan
      • Latest Headlines
      • Life & Living
      • Markets
      • Mobile
      • Movies
      • New Zealand
      • Nigeria
      • Politics
      • Scholarships
      • Science
      • South Africa
      • South America
      • Sports
      • Tech
      • Travel
      • Travel-Africa
      • UK
      • USA
      • Weather
      • World
      No Result
      View All Result

      Recent News

      US Democrats Make History by Nominating Jeffries as First Black Speaker of the House

      US Democrats Make History by Nominating Jeffries as First Black Speaker of the House

      November 18, 2026
      Stephen A. Smith Stands Firm in Defense of Trump Interview Amidst Fact-Check Criticism

      Stephen A. Smith Stands Firm in Defense of Trump Interview Amidst Fact-Check Criticism

      November 18, 2026
      Vintage Photo of Robert Pattinson and Daniel Craig Gains New Significance Amid Bond Casting Developments

      Vintage Photo of Robert Pattinson and Daniel Craig Gains New Significance Amid Bond Casting Developments

      November 18, 2026
      Top 7 Retirement Threats and Effective Strategies to Navigate Them

      Top 7 Retirement Threats and Effective Strategies to Navigate Them

      November 18, 2026
      • Home
      • Advertise With Us
      • About Us
      • Corporate
      • Consumer Rewards
      • Forum
      • Privacy Policy
      • Social Trends

      Theinsightpost ©2026 | All Rights Reserved. Theinsightpost is an Elnegy LLC company, registered in Texas, USA

      Welcome Back!

      Login to your account below

      Forgotten Password?

      Retrieve your password

      Please enter your username or email address to reset your password.

      Log In

      Add New Playlist

      We are using cookies to give you the best experience on our website.

      You can find out more about which cookies we are using or switch them off in .

      No Result
      View All Result
      • Home
      • Insight
      • Blog
      • Business
      • Entertainment
      • Health
      • Politics
      • Shop
        • Gift Shop
        • Value Shop
        • Store
        • Bargain Shop
        • Discount
      • Sports
      • Tech
      • Travel
      • USA
      • Video
      • World
        • Asia
        • Africa
        • South America
        • North America
        • Europe
        • Oceania

      Theinsightpost ©2026 | All Rights Reserved. Theinsightpost is an Elnegy LLC company, registered in Texas, USA

      The Insight Post
      Powered by  GDPR Cookie Compliance
      Privacy Overview

      This website uses cookies so that we can provide you with the best user experience possible. Cookie information is stored in your browser and performs functions such as recognising you when you return to our website and helping our team to understand which sections of the website you find most interesting and useful.

      Strictly Necessary Cookies

      Strictly Necessary Cookie should be enabled at all times so that we can save your preferences for cookie settings.

      Cookie Policy

      More information about our Cookie Policy