









Recent Cybersecurity Incidents Raise Concerns Over Infrastructure Vulnerabilities
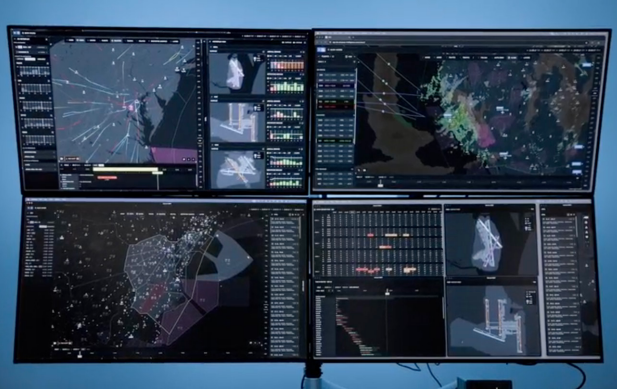
Federal Aviation Administration’s (FAA) SMART Interface
This year has seen a surge in cybersecurity incidents impacting critical infrastructure, generating unease among stakeholders in artificial intelligence (AI) and cybersecurity. Notable disruptions include the global outage of Microsoft 365 Office services on November 12 and a nationwide ground stop issued by the U.S. Federal Aviation Administration (FAA) on November 13. Additionally, problems with online banking, particularly involving Chase Bank, emerged on November 16.
Detailed Analysis of Recent Outages
Despite the widespread perception that these incidents may be linked to AI-driven cyberattacks, investigations have shown otherwise. Microsoft clarified that its service outage stemmed from a “technical issue not related to cyber or AI agents.” Subsequent reports indicated that a dormant bug in Microsoft’s systems, which had been in place since July, triggered the outage during a data re-routing process.
The FAA’s ground stop was attributed to a planned upgrade, where legacy copper wires were replaced with fiber optic cables at a remote communications site in El Dorado, Arkansas. A newly installed router became overwhelmed with connection attempts, leading to the disruption of air traffic. The Federal Bureau of Investigation (FBI) is currently examining the router as part of its due diligence.
In the case of Chase Bank, the online banking issues were linked specifically to transactions with other banks via the Zelle payment system. A spokesperson confirmed that there were no indications of malicious activity, emphasizing that the problem was not cybersecurity-related.
The Reality of Cyber Threats
While some incidents may not involve AI, the threat of cyberattacks remains ever-present. Recent reports have uncovered hacking incidents affecting refrigeration units in U.S. military commissaries, as well as targeting aerospace organizations. Google Threat Intelligence disclosed that a U.S. aerospace entity was recently targeted by malicious actors employing an open-source tool developed in China.
State-sponsored cyberattacks also pose significant risks. The FBI reported that a cyberattack on Binance, resulting in over $6 billion in theft, was executed by North Korean operatives. This sophisticated attack involved social engineering tactics and exploited vulnerabilities in employees’ systems.
Implications for Cybersecurity Practices
The evolving landscape of cyber threats highlights the need for a robust response strategy. It is essential to recognize that while AI capabilities can enhance offensive cyber operations, the fundamental principles of cybersecurity—such as maintaining legacy infrastructure and implementing sound security practices—are equally critical in mitigating risks.
The U.S. military is exploring new cybersecurity initiatives, such as Project Griffin, which aims to leverage AI for defensive purposes. However, questions persist regarding the effectiveness and safety of current systems, particularly following incidents like the FAA’s ground stop.
Key Considerations for Future Incidents
- Are initial reports consistent across sources?
- Is AI implicated, and if so, in what capacity?
- If large language models (LLMs) are involved, are they significant to the attack process?
- Did the attack utilize social engineering techniques, as seen in the Binance hack?
- Would the outcome differ if LLMs were not accessible to the attackers?
- Do reports from AI labs potentially exaggerate the role of LLMs in such incidents?
- In the absence of specific details, is a cyberattack the most plausible explanation, or could it be due to system maintenance failures?

Discussion about this post